
Regulation of Certifying Authorities, Digital Certificates and Offences
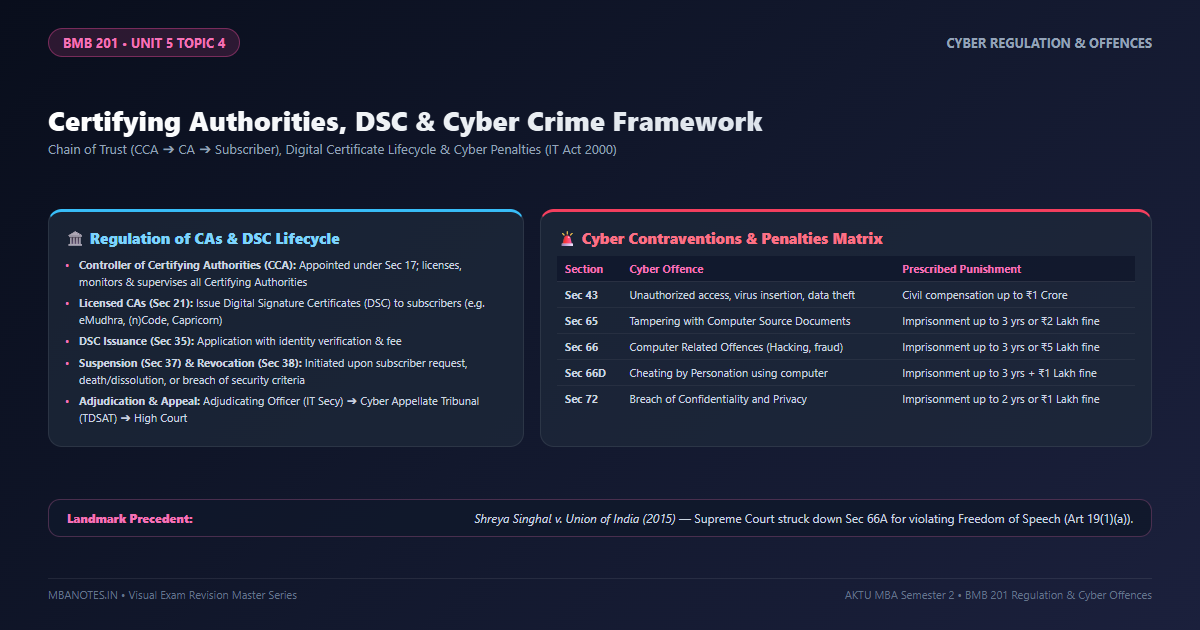
Figure 5.4: Hierarchical Trust Model of Certifying Authorities, DSC Lifecycle, and Statutory Cyber Offences Matrix.
1. Regulation of Certifying Authorities: The Hierarchical Trust Model
Digital transactions can only operate smoothly if market participants can verify that a public key genuinely belongs to the purported signer. To build this trust, the Information Technology Act 2000 establishes a Public Key Infrastructure (PKI) governed by a two-tier regulatory structure under Chapter VI (Sections 17 to 34):
The Controller of Certifying Authorities (CCA) [Sec 17]
Appointed by the Central Government, the CCA serves as the apex regulator and Root Certifying Authority of India:
• Licensing CAs: Evaluates technical, financial, and security qualifications to grant licenses to Certifying Authorities (Sec 21).
• Supervision & Auditing: Monitors CA operations, conducts mandatory security audits, and specifies cryptographic standards.
• National Repository: Maintains the National Repository of Digital Certificates (NRDC) containing all issued, suspended, and revoked certificates.
• Investigative Powers: Power to access computers, inspect source code, search premises, and intercept encryption keys.
Licensed Certifying Authorities (CAs) [Sec 21-34]
CAs are trusted commercial or governmental intermediaries licensed to issue Digital Signature Certificates (e.g., eMudhra, TCS, (n)Code, Sify, Capricorn):
• Certification Practice Statement (CPS): Operates under an approved CPS detailing technical protocols.
• Identity Verification: Rigorously validates subscriber identity and credentials prior to issuing a certificate.
• Suspension & Revocation: Power to suspend or revoke licenses if a CA fails to adhere to security standards or violates provisions (Sec 25).
2. Digital Signature Certificate (DSC) Lifecycle [Sections 35 to 39]
Chapter VII specifies the legal rules governing the creation, maintenance, and termination of Digital Signature Certificates:
A. Application & Issuance [Section 35]
Any person may make an application to the Certifying Authority for the grant of a Digital Signature Certificate accompanied by prescribed fees and a Certification Practice Statement compliance declaration. Upon verification, the CA issues the DSC containing the subscriber’s name, public key, validity period, serial number, and the digital signature of the CA.
B. Suspension of DSC [Section 37]
The Certifying Authority may suspend a Digital Signature Certificate:
• Upon request by the subscriber or any person duly authorized by him; or
• If the CA is of the opinion that the suspension is necessary in public interest.
Statutory Restriction: A DSC cannot be suspended for a period exceeding 15 days unless the subscriber has been given a reasonable opportunity of showing cause.
C. Revocation of DSC [Section 38]
A Certifying Authority shall revoke a Digital Signature Certificate upon:
1. Request by the subscriber or his legal representative.
2. Death of the subscriber (for individuals) or winding up / dissolution (for corporations).
3. Discovery that a material fact represented in the application was false or concealed.
4. Compromise of the private key or certifying authority’s security system.
3. Civil Contraventions & Adjudication [Sections 43 to 47]
Chapter IX of the IT Act establishes civil liability for unauthorized access, data damage, and digital disruption. Unlike criminal trials requiring proof beyond reasonable doubt, civil contraventions under Section 43 are adjudicated by an Adjudicating Officer (appointed under Sec 46, typically the State IT Secretary):
| Section | Contravention Details | Statutory Remedy / Compensation |
|---|---|---|
| Section 43(a)-(j) | Unauthorized access, downloading or copying data, introducing computer contaminants/viruses, damaging computer databases, disrupting computer networks, denying authorized access (DoS attack), or stealing code. | Liable to pay compensation up to ₹1 Crore to the affected person. |
| Section 43A | Corporate failure to protect Sensitive Personal Data or Information (SPDI) through reasonable security practices, causing wrongful loss or wrongful gain. | Liable to pay unlimited damages by way of compensation to the affected person. |
| Sections 48-64 | Appeals against Adjudicating Officer orders preferred to Cyber Appellate Tribunal (now merged with TDSAT – Telecom Disputes Settlement and Appellate Tribunal). | Appeal must be filed within 45 days; further appeal lies to the High Court on questions of law (Sec 62). |
4. Criminal Cyber Offences & Penalties [Chapter XI]
Chapter XI of the IT Act criminalizes deliberate cyber wrongdoing, investigated by police officers not below the rank of Inspector (Sec 78):
| Section | Cyber Crime Description | Prescribed Criminal Punishment |
|---|---|---|
| Section 65 | Tampering with Computer Source Documents (concealing, destroying, or altering source code required by law). | Imprisonment up to 3 years, or fine up to ₹2 Lakhs, or both. |
| Section 66 | Computer Related Offences / Hacking (committing any act referred to in Sec 43 dishonestly or fraudulently). | Imprisonment up to 3 years, or fine up to ₹5 Lakhs, or both. |
| Section 66A | Punishment for sending offensive messages through communication service. | STRUCK DOWN as unconstitutional by Supreme Court in Shreya Singhal (2015). |
| Section 66C | Identity Theft (fraudulent use of electronic signature, password, or unique identification feature). | Imprisonment up to 3 years and fine up to ₹1 Lakh. |
| Section 66D | Cheating by Personation using computer resource (phishing, spoofing, impersonation fraud). | Imprisonment up to 3 years and fine up to ₹1 Lakh. |
| Section 66E | Violation of Privacy (capturing, publishing, or transmitting images of private areas of a person without consent). | Imprisonment up to 3 years, or fine up to ₹2 Lakhs, or both. |
| Section 72 | Breach of Confidentiality and Privacy by person having authorized access under the Act. | Imprisonment up to 2 years, or fine up to ₹1 Lakh, or both. |
6. Corporate Case Vignette: Freedom of Speech vs. Cyber Regulation
Shreya Singhal v. Union of India (AIR 2015 SC 1523)
Fact Summary: Two young women were arrested by police under Section 66A of the IT Act for posting and liking comments on Facebook questioning the complete shutdown of Mumbai city following the demise of a political leader. A public interest litigation was filed by law student Shreya Singhal challenging the constitutional validity of Section 66A, which criminalized sending “offensive” or “menacing” messages via computer systems.
Legal Ratio & Judgment: The Supreme Court struck down Section 66A in its entirety as unconstitutional. Justices J. Chelameswar and R.F. Nariman held that terms like “grossly offensive” and “annoyance” were unconstitutionally vague, overbroad, and had a chilling effect on the fundamental Right to Freedom of Speech and Expression under Article 19(1)(a) of the Constitution. The Court clarified that reasonable restrictions under Article 19(2) cannot be invoked for mere advocacy or political dissent.
7. AKTU Examination Focus & University PYQs
Review these university exam questions formatted strictly to the AKTU evaluation pattern:
- Q1: Who is the Controller of Certifying Authorities (CCA) under the IT Act 2000?
Model Answer: Appointed under Section 17 by the Central Government, the CCA is the apex statutory authority that licenses, monitors, and supervises all Certifying Authorities issuing Digital Signature Certificates. - Q2: State two grounds for the revocation of a Digital Signature Certificate under Section 38.
Model Answer: (1) Upon request by the subscriber or death/dissolution of the subscriber, and (2) If a material fact in the application was false or the private key was compromised. - Q3: What was the constitutional ruling in Shreya Singhal v. Union of India (2015)?
Model Answer: The Supreme Court struck down Section 66A of the IT Act as unconstitutional for violating the fundamental right to free speech under Article 19(1)(a) due to vagueness and overbreadth.
- Q4: Explain the regulatory framework governing Certifying Authorities in India. Discuss the procedure for obtaining a license, powers of the Controller, and the lifecycle of Digital Signature Certificates.
Answer Framework: Detail the role of CCA under Section 17. Explain the licensing process for CAs under Sections 21-24. Discuss the DSC lifecycle from application (Sec 35) to suspension (Sec 37) and revocation (Sec 38). Outline duties of subscribers to safeguard private keys (Sec 42).
- Q5: Distinguish between civil contraventions under Section 43 and criminal cyber offences under Chapter XI of the Information Technology Act 2000. Detail the provisions relating to hacking, identity theft, and cheating by personation.
Answer Framework: Distinguish between civil adjudication (Sec 43/46 before Adjudicating Officer with compensation up to ₹1 Cr) and criminal prosecution (Chapter XI before courts with imprisonment). Detail hacking under Sec 66, identity theft under Sec 66C, and cheating by personation (phishing) under Sec 66D. Discuss the landmark Shreya Singhal case regarding Sec 66A.
Discussion & Questions
0 CommentsAcademic insights, questions, and conceptual clarifications from students & faculty.
No questions or comments yet
Have a doubt about this topic, an exam tip, or a conceptual perspective? Start the discussion below!
Leave a Comment / Ask a Question
Your email address will not be published. Required fields are marked *